

At AIBC Rome, MiCA’s Disclosure Rules and the Case for Interoperability
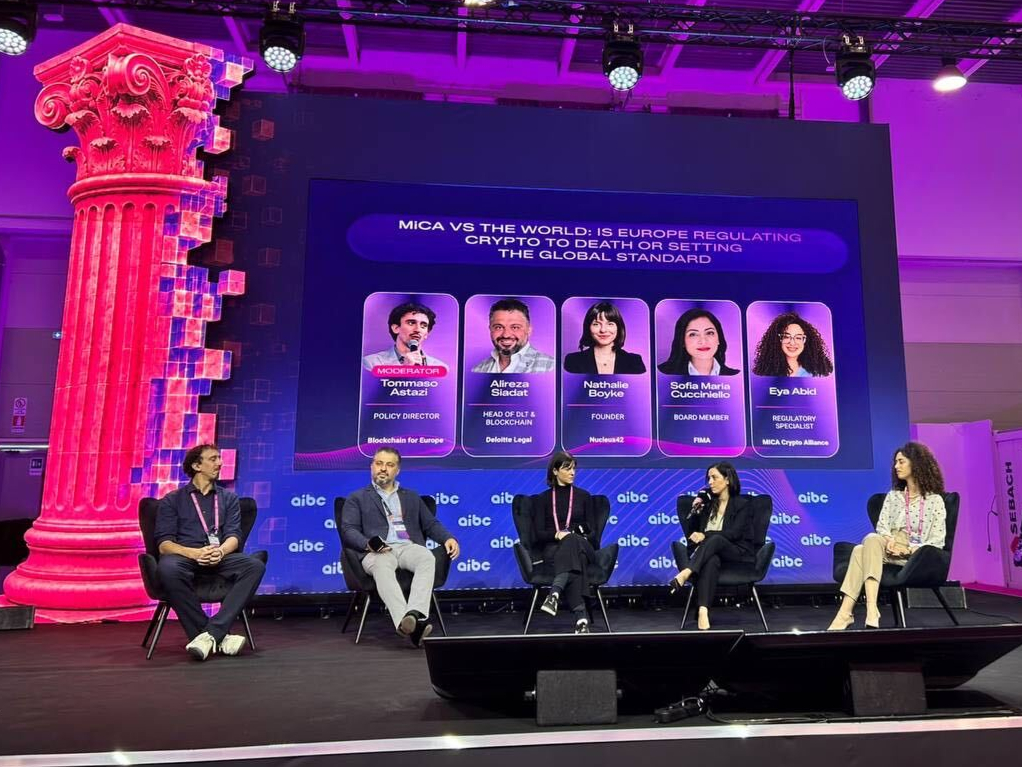
AIBC World brought speakers and delegates to Rome from 2 to 5 November to discuss AI, blockchain and digital assets. On Day 1, Eya Abid, Regulatory Specialist at the MiCA Crypto Alliance, joined “MiCA vs The World: Is Europe Regulating Crypto to Death or Setting the Global Standard.” The session compared Europe’s approach with evolving frameworks in the US, the UK and Asia, and asked whether MiCA will shape the global rulebook or fragment the crypto landscape. The panel was moderated by Tommaso Astazi of Blockchain for Europe, with Nathalie Boyke of nucleus42, Alireza Siadat of Deloitte Legal and Sofia Maria Cucciniello of Crypto.com. Eya’s contribution centred on disclosure.
A Prescriptive Regime, Not an Isolated One
MiCA’s detailed white paper requirements, with their technical standards and templates, give a relatively clear roadmap of what regulators expect to know about a crypto-asset. Eya’s own work on crypto-asset regulation began with MiCA, which she found useful for understanding how other jurisdictions’ disclosure requirements differ. A white paper sets out the asset’s characteristics, the project and the risks, and for most crypto-assets it is notified to the national authority at least 20 working days before publication, not approved in advance. The detail has a cost: implementing and standardising the disclosures, including the introduction of XBRL, is demanding. It does not, in her view, isolate Europe, because other jurisdictions have simply chosen different philosophies.
The UK’s new regime identifies the key areas of information that QCDDs and SDDs must cover but does not prescribe a standardised template. The US proposals focus on specific, material disclosures rather than replicating MiCA’s structure. Sustainability is another difference. MiCA addresses it explicitly, a requirement the Alliance has not found across all the frameworks it has examined.
The risk disclosures in a white paper is a form of consumer protection, though not a guarantee. MiCA does not make an asset risk-free, and crypto-assets are not covered by the usual bank deposit guarantee. On the panel’s question of whether Europe is regulating crypto to death, the clearest benefit for a first-time buyer is knowing who they are dealing with. An authorised provider must meet standards on governance, safeguarding client assets and conflicts of interest.
From Alignment to Interoperability
The next step for MiCA 2.0, in Eya’s opinion, is practical interoperability between jurisdictions: more structured dialogue on cross-border market access and disclosure, so that businesses do not start from scratch in every new market. MiCA’s passporting already lets a provider authorised in one Member State offer its services across the EU, which can reduce duplicated compliance costs and make expansion easier. She would like to see that principle taken further, beyond the EU. The Maltese regulator’s openness, at Fintech30 in September, to cooperation with third-country jurisdictions, including Bermuda, is one encouraging sign.
The Alliance raises interoperability often in its consultation responses, and is now working on its own contribution: a multi-purpose disclosure document that could accommodate MiCA white paper requirements while aligning with the UK’s QCDD regime. One document cannot automatically satisfy every jurisdiction, she cautioned, and each framework must still be respected.
Outlook
Clarity matters, and clarity combined with cross-border interoperability is what supports a competitive European market. Eya measures MiCA’s success by the trust it creates and the innovation it enables, not by the number of rules introduced. Her test for any rule is whether it provides meaningful transparency, accountability or protection, or only duplication.


